How it works
How your family actually gets in.
The hardest question in this category has a simple answer: a recovery kit you control, not a company login. Here's exactly how the handoff works.
“Bequest has no server. Your family gets in with the recovery kit you give them — not a login that could lapse.”
- 01
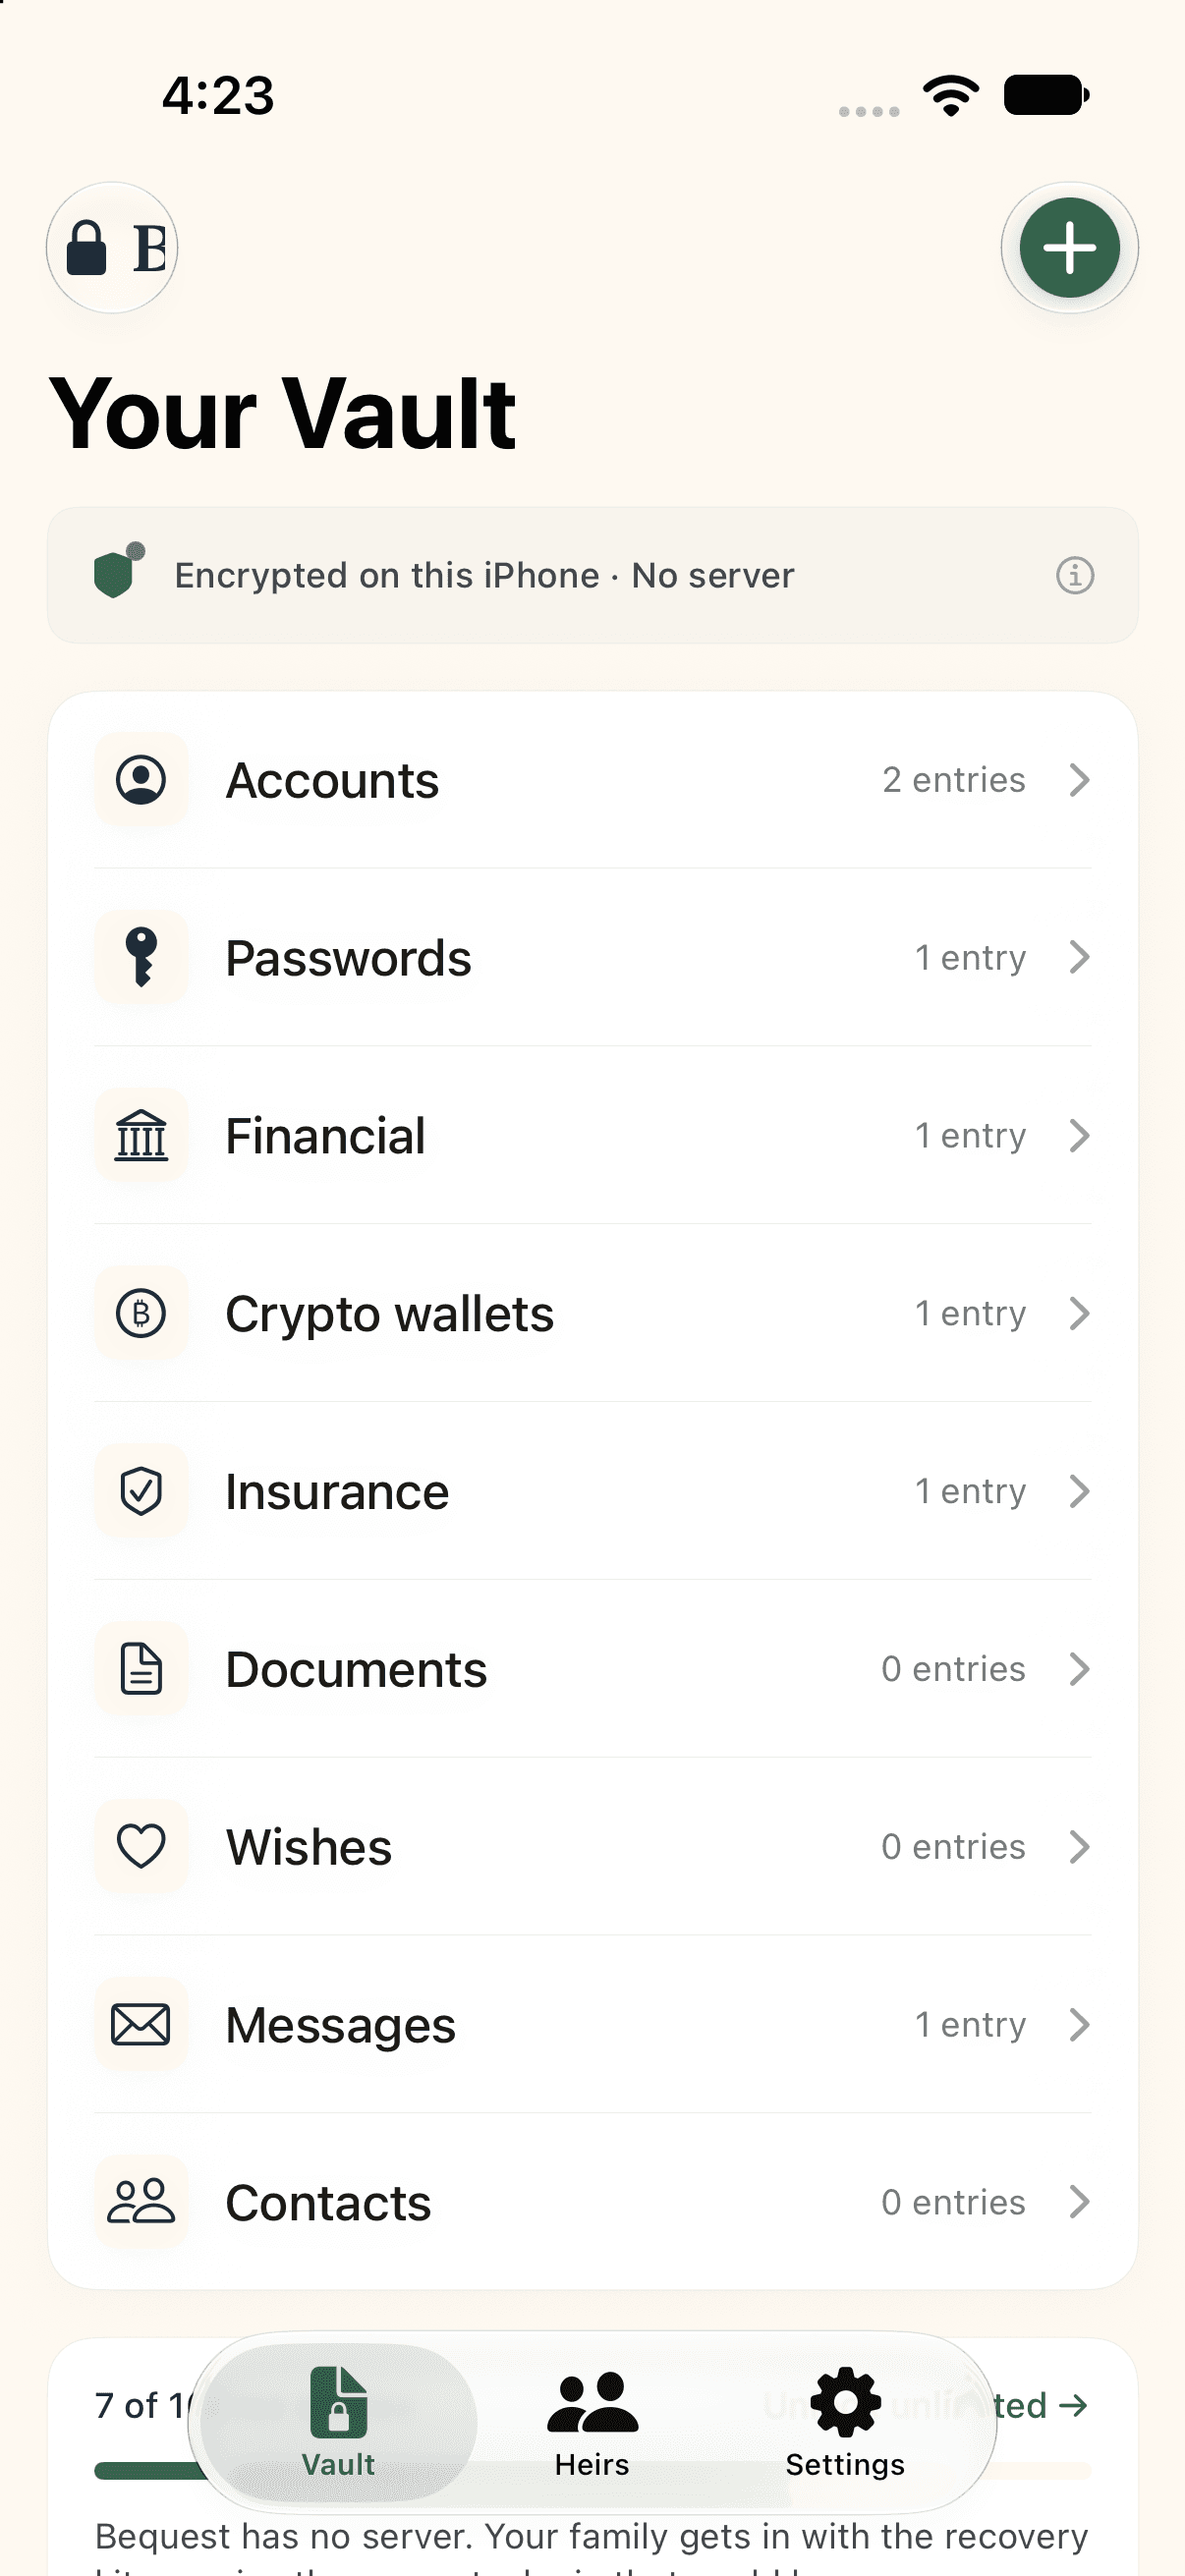
You fill the vault.
Add accounts, passwords, financial and crypto details, insurance, documents, wishes and a last message. Each entry is encrypted on your iPhone the moment you save it.
- 02
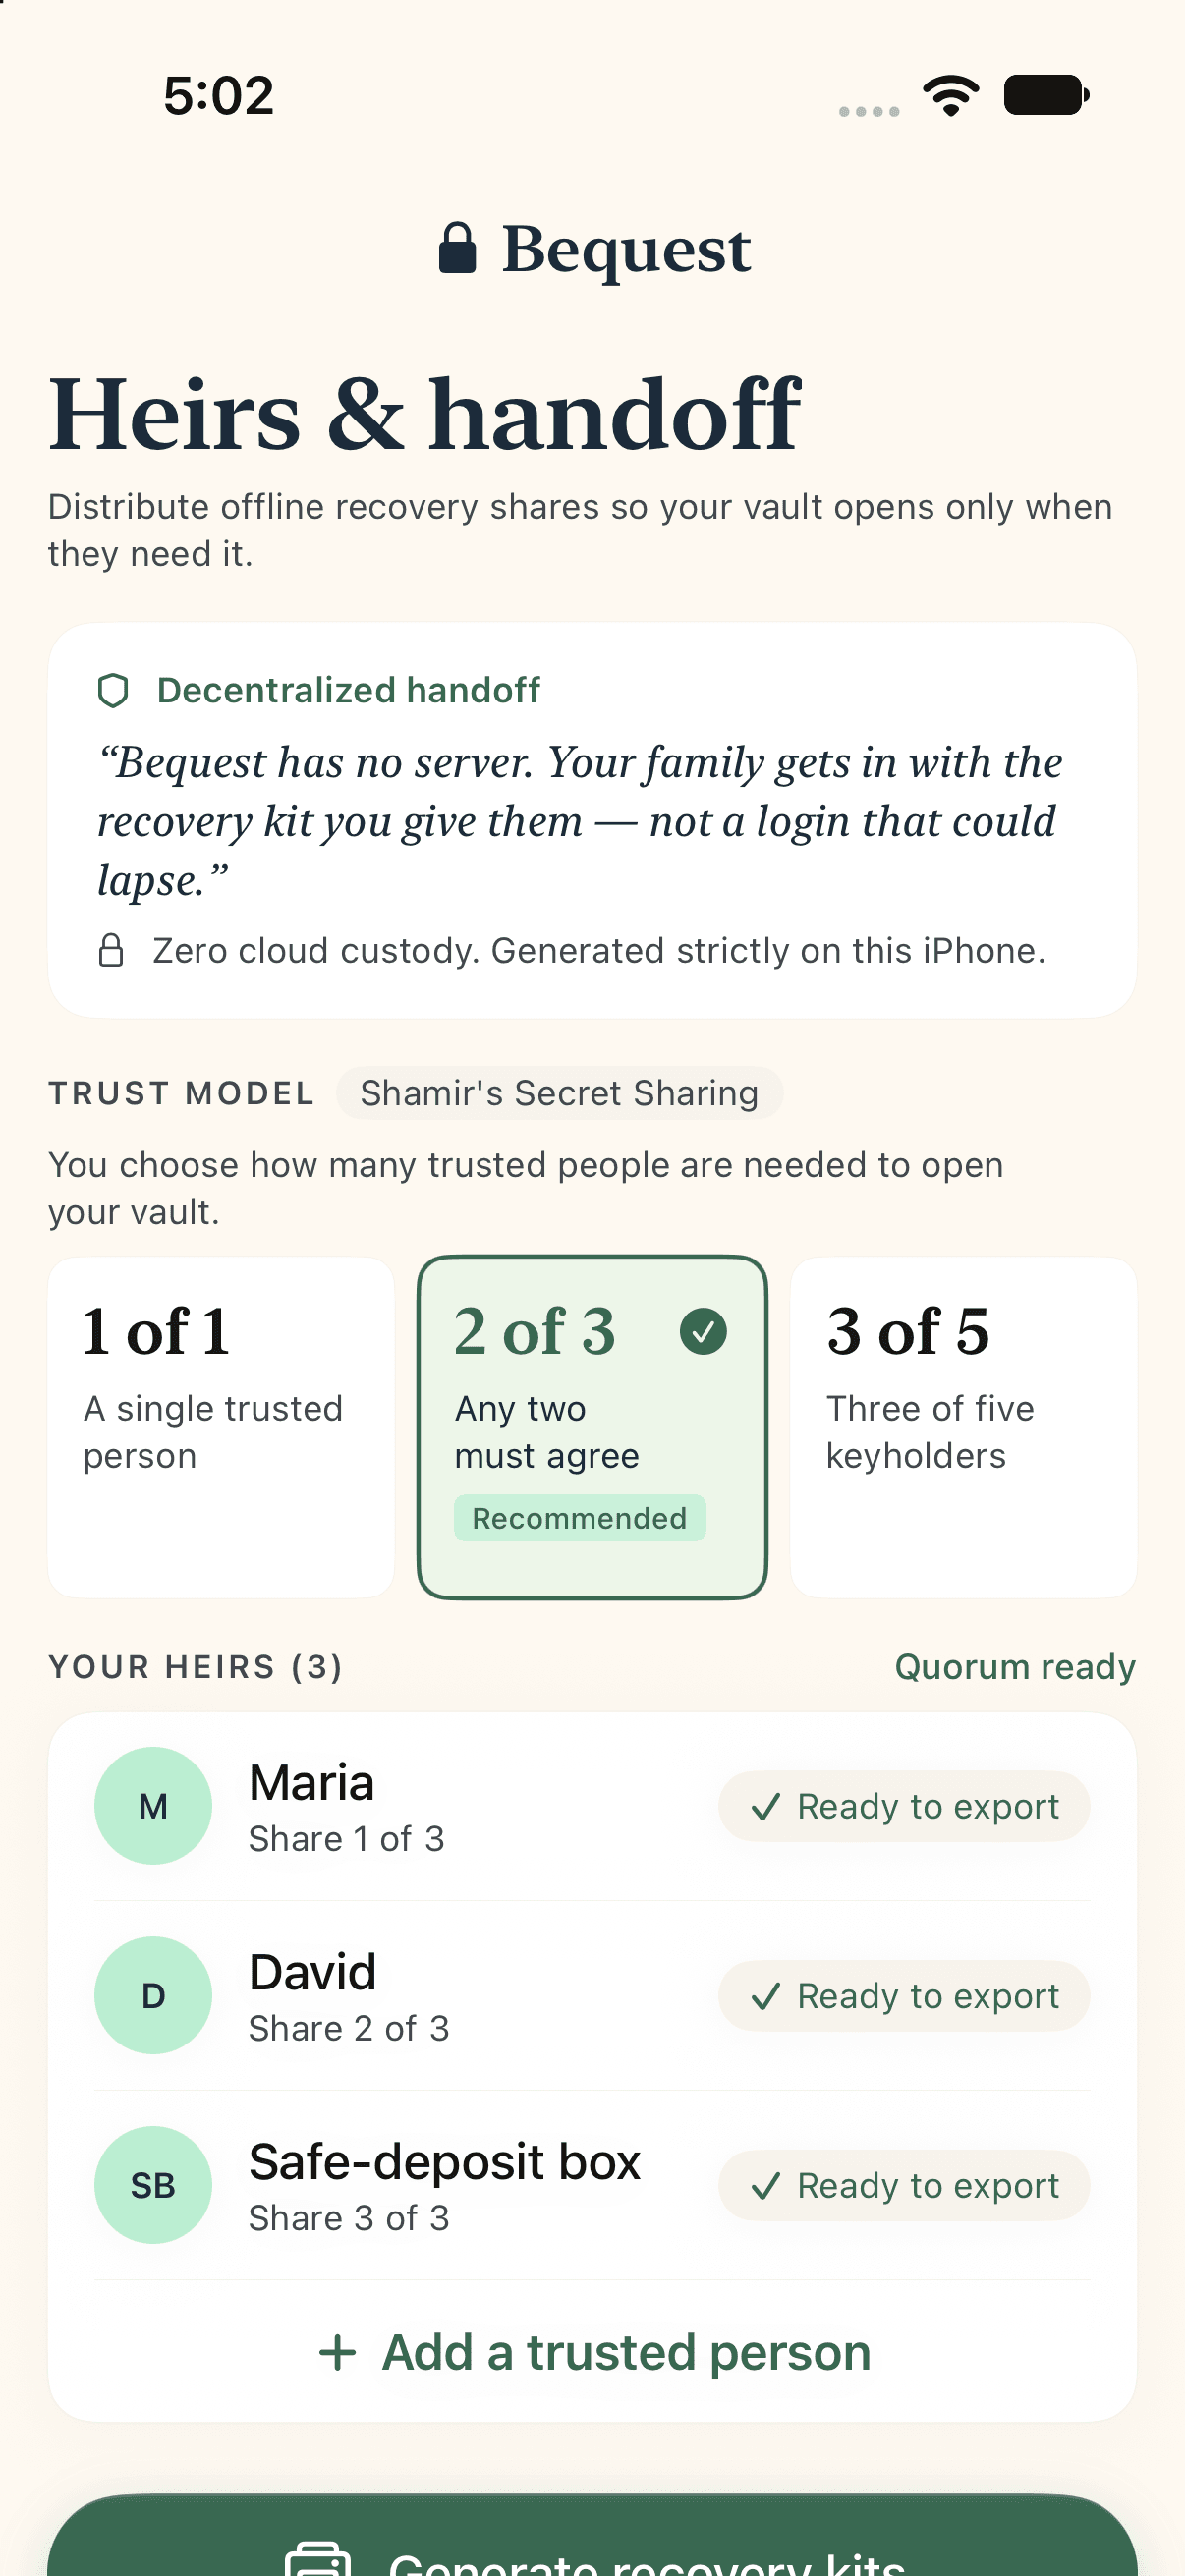
You choose who gets in, and how.
Pick a trust model: one trusted person, or a quorum like 2 of 3. Bequest splits your recovery key into shares using Shamir's Secret Sharing — no single person can open the vault alone.
- 03
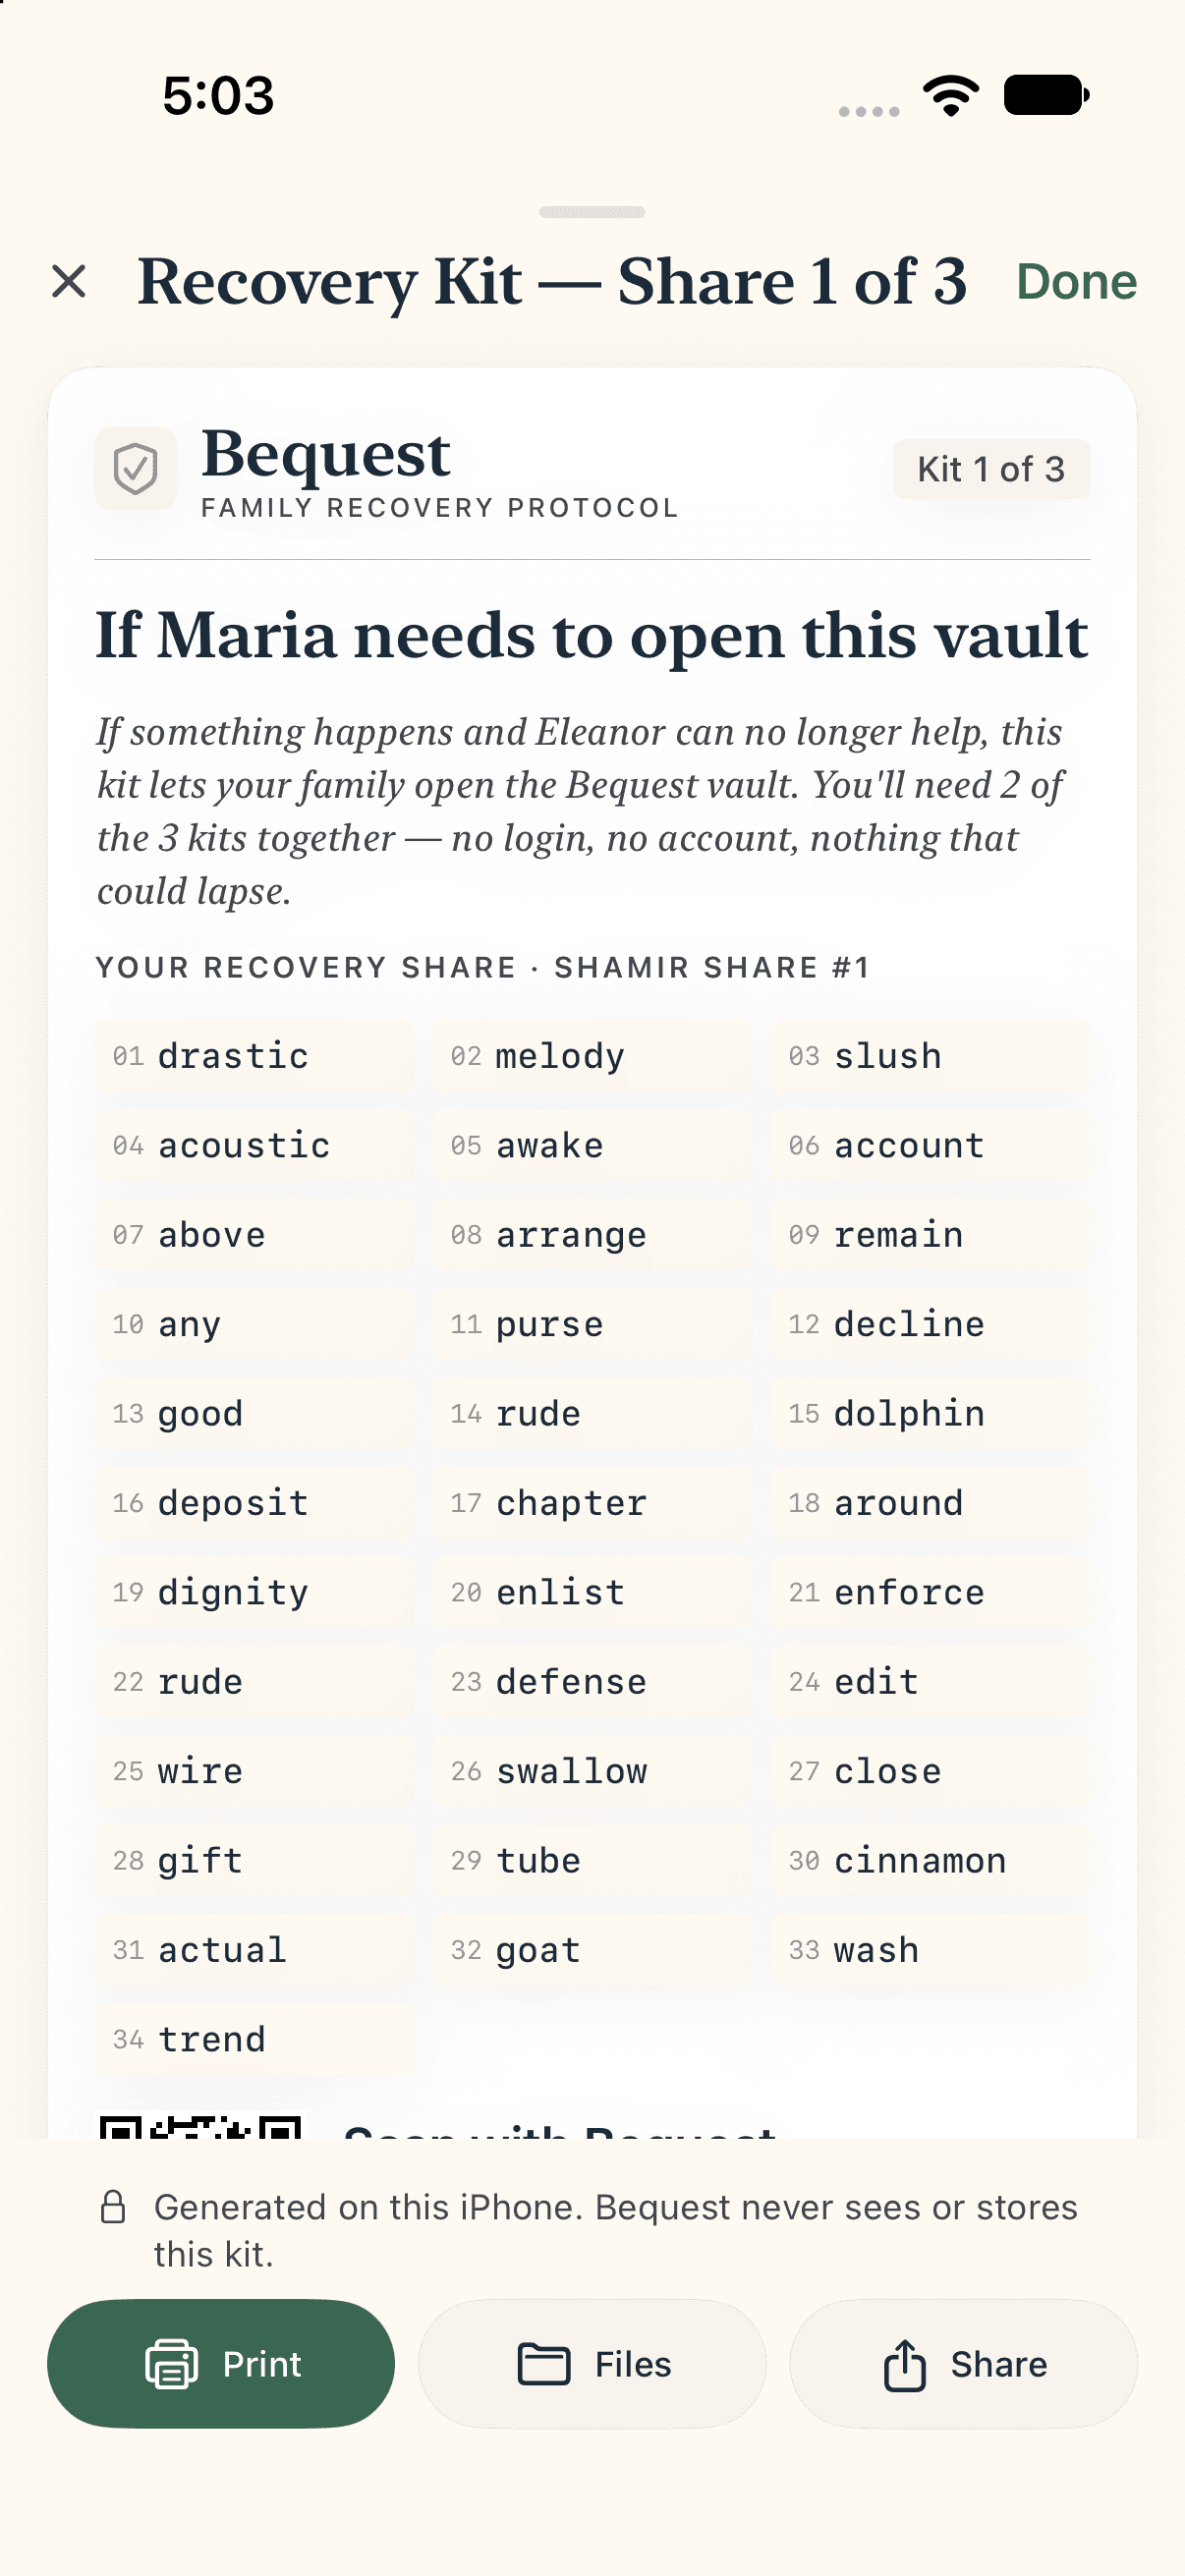
You print the recovery kits.
Each share becomes a printable kit: 12 words, a QR code, plain instructions, and where the encrypted backup lives. You hand them to the people you trust. Bequest never sees or stores them.
- 04
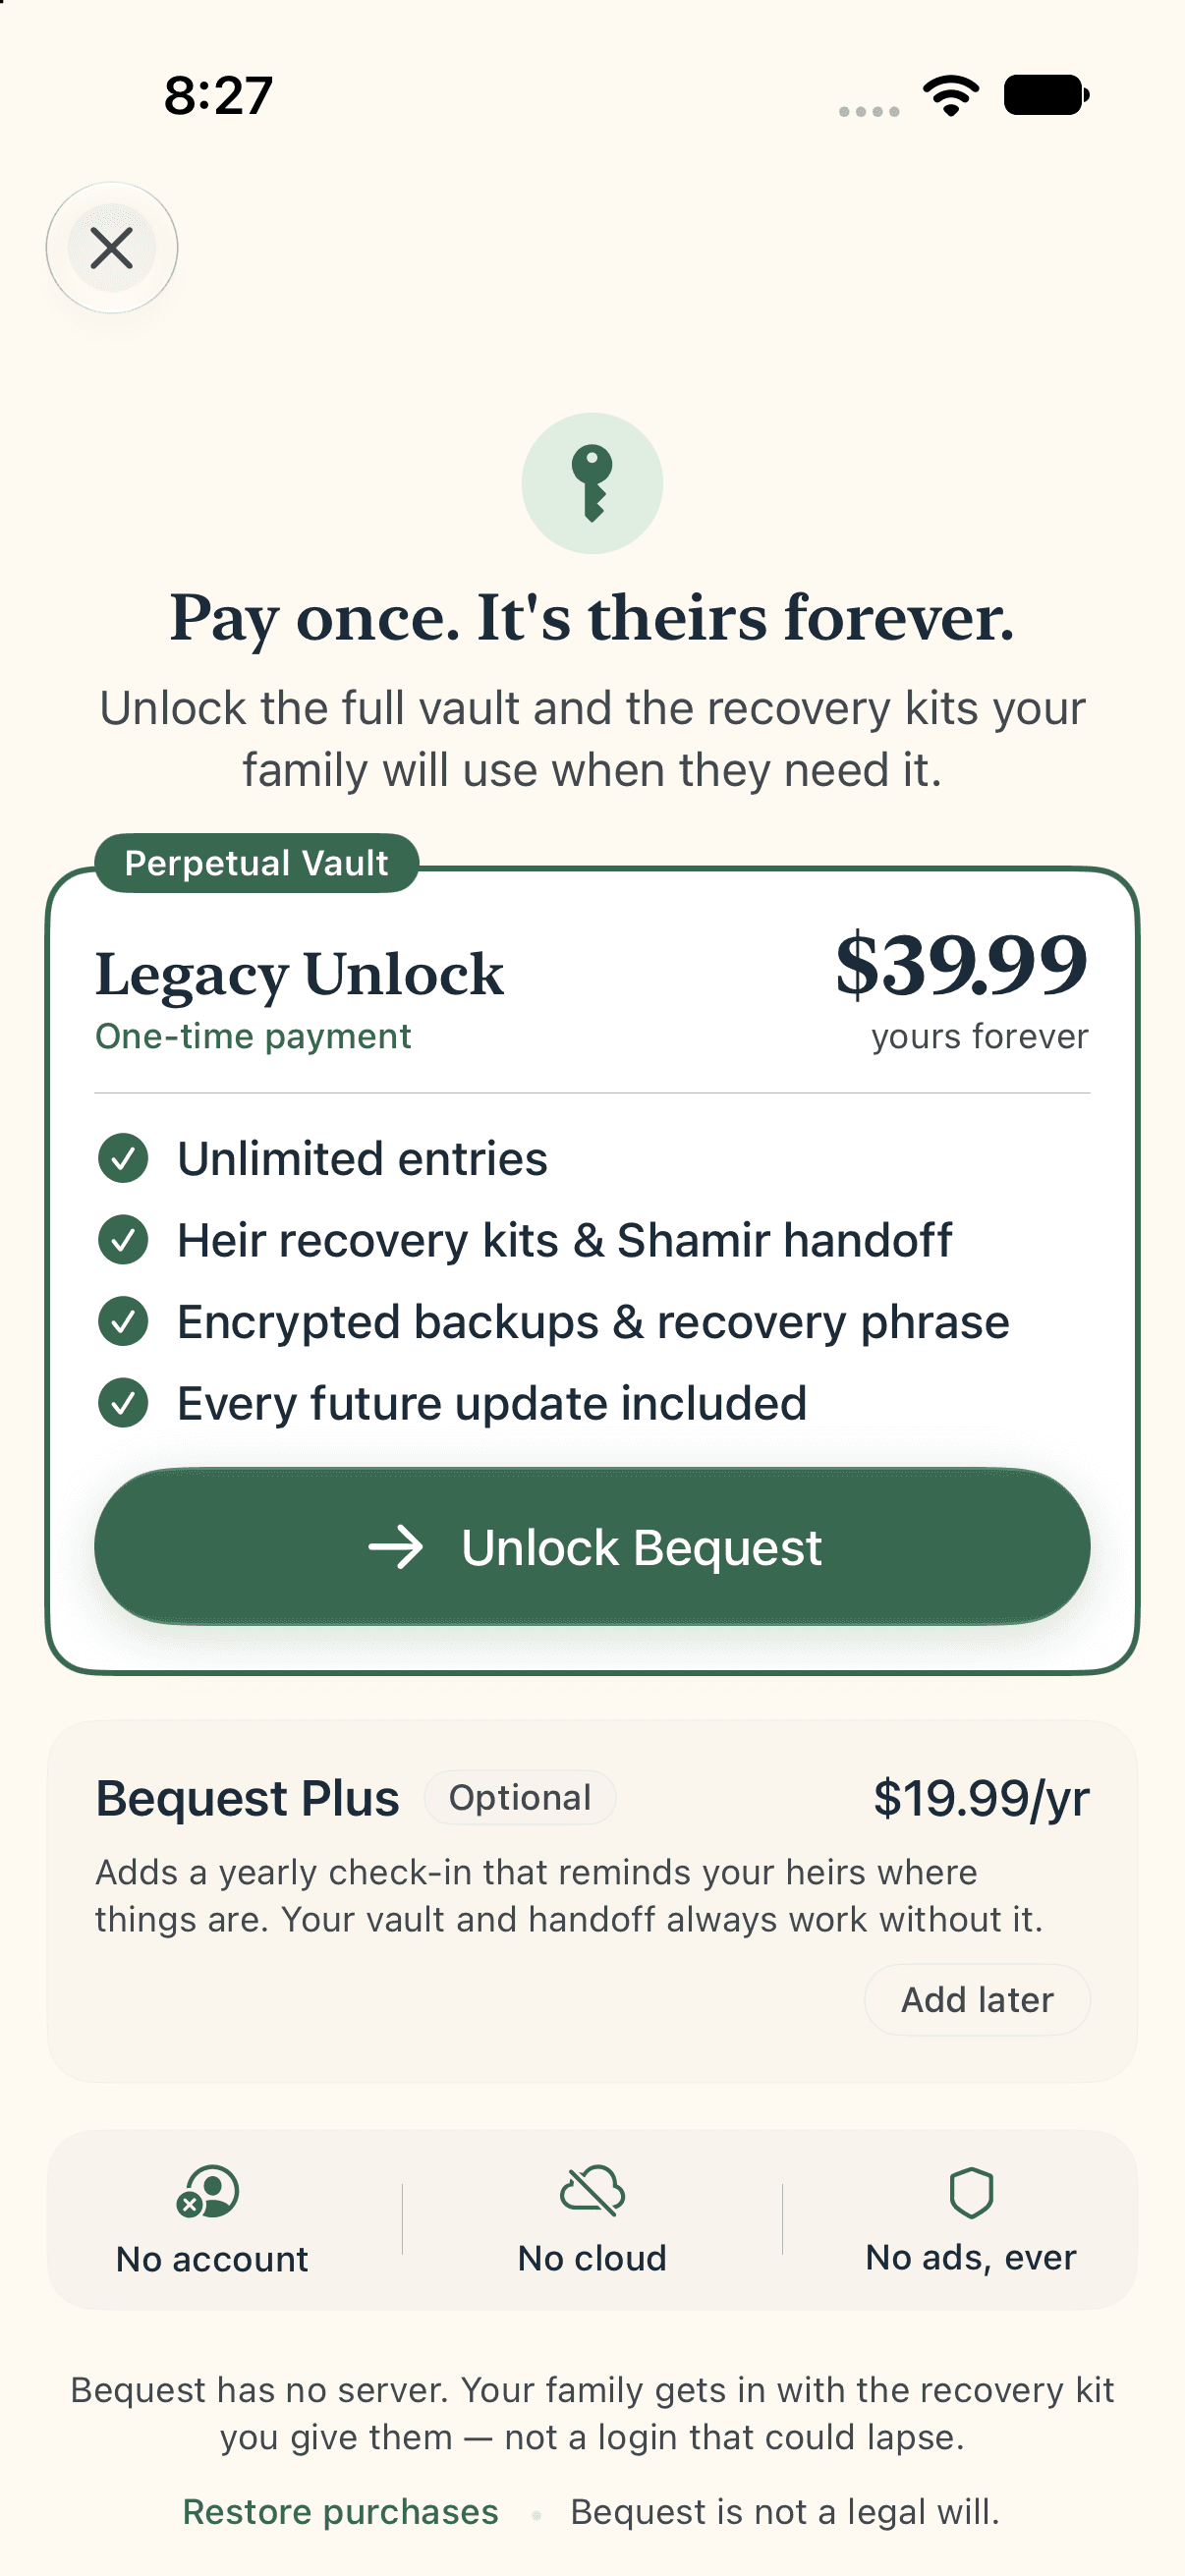
Later, your family opens the vault — without us.
On their own iPhone, they load the encrypted backup and combine the required kits. The vault opens read-only, honoring each entry's release timing. No account, no network — verifiable in airplane mode.
Why this matters
A login can lapse. A company can disappear. Your kit can't.
Bequest has no server, so there's no account to expire and nothing to breach. The handoff depends only on the kits in your family's hands.